📘 들어가며
이전 글에서 우리는 사용자의 인증(Authentication) 흐름을 완성했습니다.
이제 인증된 사용자가 무엇을 할 수 있는가, 즉 인가(Authorization)를 다룰 차례입니다.
Spring Security는 인가를 세 가지 수준으로 제공합니다:
- 엔드포인트(API) 수준 –
hasAuthority()/hasRole() - 메소드 수준 –
@PreAuthorize,@PostAuthorize - 필터 수준 – 커스텀 필터를 통한 요청 전/후 처리
이번 글에서는 이 세 수준을 하나의 축으로 연결해,
권한 기반 접근 제어 → 역할 기반 접근 제어 → 커스텀 필터 → 메소드 보안의 전체 흐름을 완성합니다.
#1. 인증 vs 인가
| 구분 | 인증 (Authentication) | 인가 (Authorization) |
|---|---|---|
| 목적 | “누구인가?” | “무엇을 할 수 있는가?” |
| 검증 대상 | 신원 (ID, 비밀번호, 토큰 등) | 권한(Role, Authority) |
| 실패 시 HTTP 코드 | 401 Unauthorized | 403 Forbidden |
| 시점 | 항상 먼저 수행 | 인증 후 수행 |
| 예시 | 여권 검사 | 탑승 게이트 체크 |
✈️ 비유
- 여권 검사: 신분을 확인하는 인증 단계
- 탑승 게이트: 목적지 티켓을 확인하는 인가 단계
#2. Spring Security 인가의 핵심 구성
Spring Security는 인가를 권한(GrantedAuthority) 단위로 관리합니다.
✅ GrantedAuthority 인터페이스
public interface GrantedAuthority {
    String getAuthority();
}
모든 권한/역할 정보는 문자열 형태로 저장됩니다.
✅ SimpleGrantedAuthority 구현체
GrantedAuthority auth = new SimpleGrantedAuthority("VIEWACCOUNT");
role이라는 필드를 갖지만, 권한(Authority)과 역할(Role) 모두 저장 가능UserDetails.getAuthorities()를 통해 불러옵니다.
#3. 권한 테이블 설계
기존 customer 테이블은 하나의 role 컬럼만을 가졌습니다.
이를 확장하여 1:N 관계로 여러 권한을 저장할 수 있습니다.
CREATE TABLE authorities (
  id BIGINT AUTO_INCREMENT PRIMARY KEY,
  customer_id BIGINT,
  name VARCHAR(50),
  FOREIGN KEY (customer_id) REFERENCES customer(id)
);
예시 데이터
| id | customer_id | name |
|---|---|---|
| 1 | 1 | VIEWACCOUNT |
| 2 | 1 | VIEWCARDS |
| 3 | 1 | VIEWBALANCE |
| 4 | 1 | VIEWLOANS |
한 고객이 여러 권한을 가질 수 있도록 설계
#4. 엔티티 매핑 구조

✅ Authority 엔티티 예시
@Entity
@Table(name = "authorities")
@Getter @Setter
public class Authority {
    @Id @GeneratedValue(strategy = GenerationType.IDENTITY)
    private Long id;

    private String name;

    @ManyToOne
    @JoinColumn(name = "customer_id")
    private Customer customer;
}
✅ Customer 엔티티 내 관계 추가
@OneToMany(mappedBy = "customer", fetch = FetchType.EAGER)
private Set<Authority> authorities;
#5. 권한 정보 로딩 로직
✅ EazyBankUserDetailsService
@Override
public UserDetails loadUserByUsername(String username) {
    Customer customer = repo.findByEmail(username).orElseThrow();

    List<GrantedAuthority> authorities = customer.getAuthorities().stream()
        .map(a -> new SimpleGrantedAuthority(a.getName()))
        .toList();

    return new User(customer.getEmail(), customer.getPassword(), authorities);
}
DB에서 Authority 엔티티를 읽어와 SimpleGrantedAuthority로 변환인증 성공 시 Authentication 객체의 authorities 필드에 저장됨
#6. Spring Security 인가 설정
ProjectSecurityConfig 내에서 각 API별로 접근 권한을 지정합니다.
.authorizeHttpRequests(auth -> auth
    .requestMatchers("/myAccount").hasAuthority("VIEWACCOUNT")
    .requestMatchers("/myBalance").hasAnyAuthority("VIEWBALANCE", "VIEWACCOUNT")
    .requestMatchers("/myLoans").hasAuthority("VIEWLOANS")
    .requestMatchers("/myCards").hasAuthority("VIEWCARDS")
    .requestMatchers("/user").authenticated()
);
✅ 주요 메소드 요약
| 메소드 | 설명 |
|---|---|
hasAuthority("A") | 특정 권한 보유 시 접근 허용 |
hasAnyAuthority("A","B") | 여러 권한 중 하나라도 있으면 허용 |
access(expression) | SpEL 기반의 복잡한 조건 구성 가능 |
#7. 권한 vs 역할
| 구분 | 권한(Authority) | 역할(Role) |
|---|---|---|
| 의미 | 세밀한 동작 단위 (예: VIEWACCOUNT) | 여러 권한의 묶음 (예: ROLE_USER) |
| 접두사 | 없음 | ROLE_ (자동 인식됨) |
| Spring Security 설정 | hasAuthority("VIEWACCOUNT") | hasRole("USER") |
| 데이터베이스 | VIEWACCOUNT, VIEWBALANCE | ROLE_USER, ROLE_ADMIN |
🧩 역할을 사용하면 보안 구성을 단순화할 수 있지만,
세밀한 API 제어가 필요할 땐 권한 기반 제어가 더 적합합니다.
#8. 권한 부여 실패 처리
403 Forbidden이 반환될 때, 백엔드에서 추가 처리를 할 수도 있습니다.
Spring Security는 이때 AuthorizationDeniedEvent를 발행합니다.
@Component
@Slf4j
public class AuthorizationEvents {

    @EventListener
    public void onDenied(AuthorizationDeniedEvent event) {
        Authentication auth = event.getAuthentication().get();
        log.error("Authorization denied for user: {} -> {}",
            auth.getName(), event.getAuthorizationDecision());
    }
}
✅ 이메일 알림, 감사 로그, DB 기록 등 커스텀 후처리 가능
#9. Security Filter Chain 이해
모든 요청은 Spring Security 필터 체인을 통과합니다.
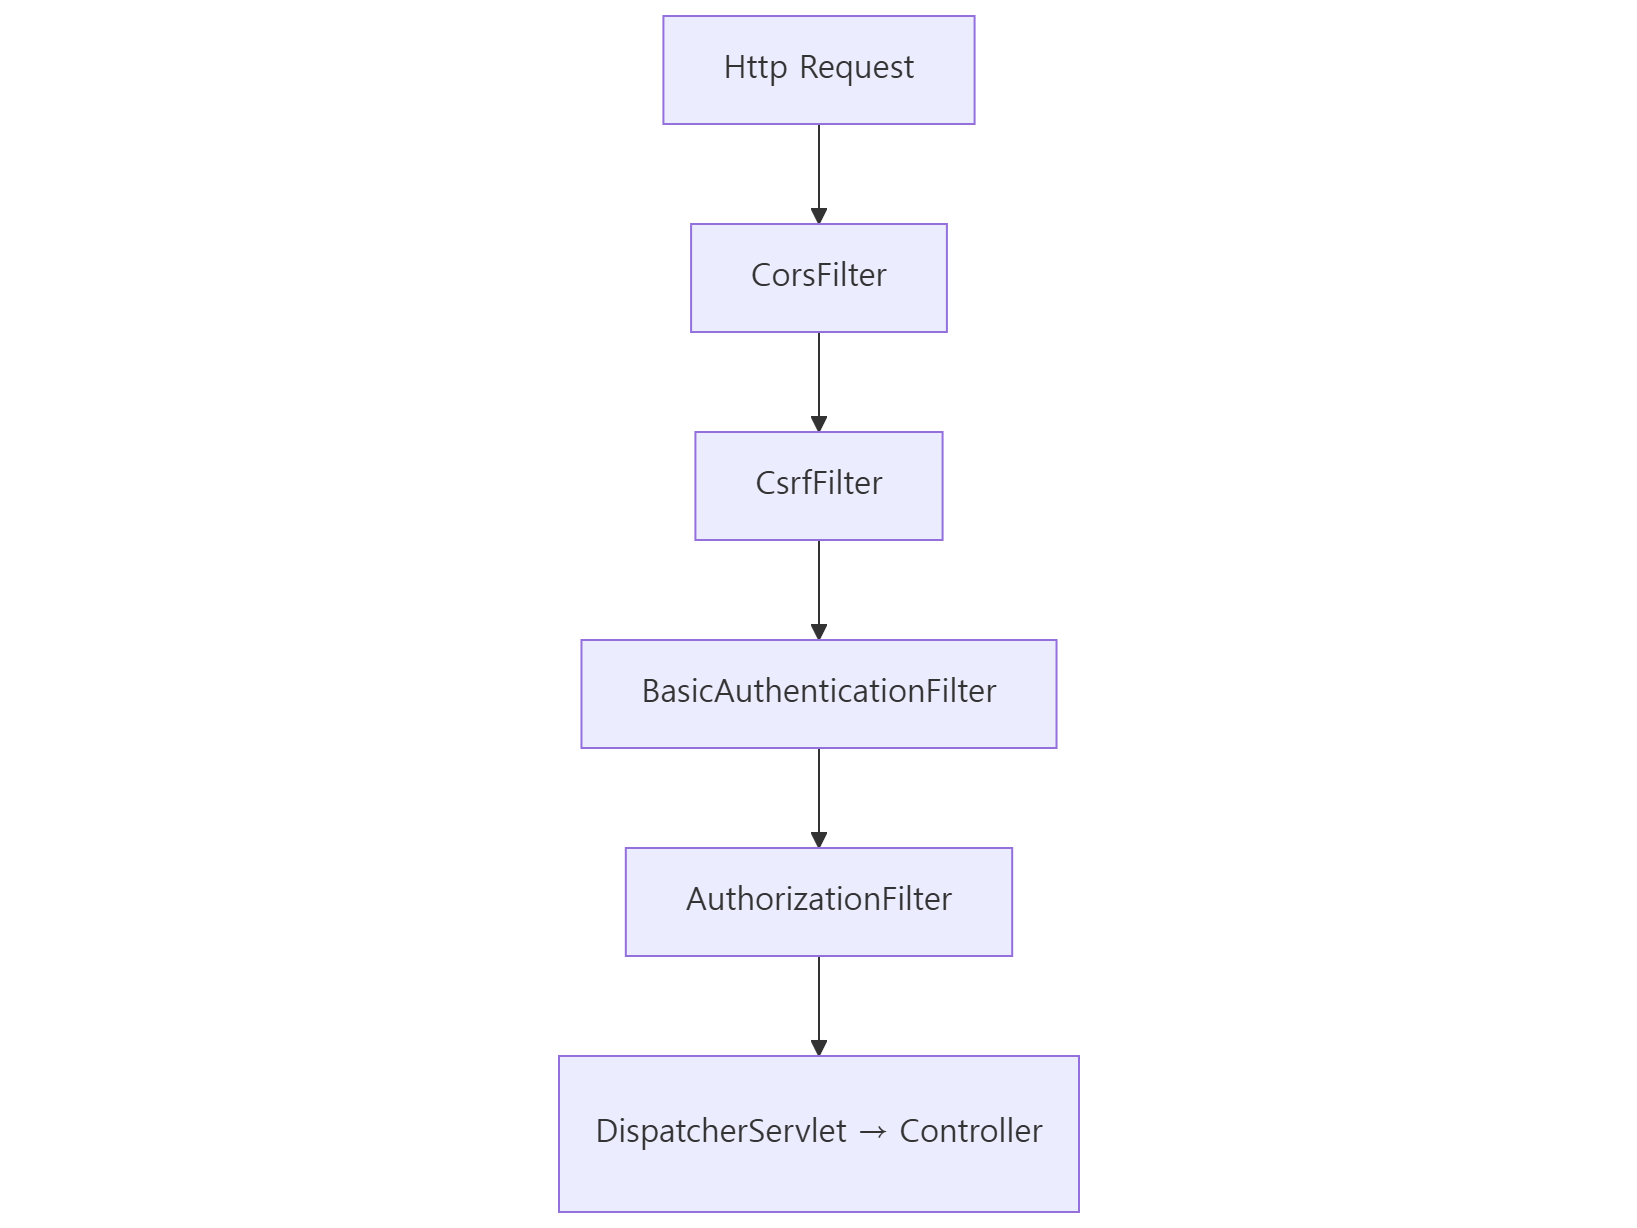
FilterChainProxy가 내부적으로 모든 필터를 관리하며
각 필터는 인증, 인가, 로깅, CSRF 등을 담당합니다.
#10. 커스텀 필터 주입
Spring Security는 다음 메소드로 필터를 주입할 수 있습니다:
| 메소드 | 실행 위치 | 설명 |
|---|---|---|
addFilterBefore() | 지정 필터 이전 | 인증 전 로직 (입력 검증, 요청 분석 등) |
addFilterAfter() | 지정 필터 이후 | 인증 후 로직 (로그, 감사 등) |
addFilterAt() | 동일 위치 | 순서 불명확 (권장 ❌) |
✅ 예시 1) RequestValidationBeforeFilter
@Component
public class RequestValidationBeforeFilter implements Filter {
    @Override
    public void doFilter(ServletRequest request, ServletResponse response, FilterChain chain)
            throws IOException, ServletException {

        HttpServletRequest req = (HttpServletRequest) request;
        String header = req.getHeader(HttpHeaders.AUTHORIZATION);

        if (header != null && header.toLowerCase().contains("test")) {
            ((HttpServletResponse) response).setStatus(HttpServletResponse.SC_BAD_REQUEST);
            return;
        }
        chain.doFilter(request, response);
    }
}
이메일에 test가 포함되면 인증 전 차단
addFilterBefore(RequestValidationBeforeFilter.class, BasicAuthenticationFilter.class);
✅ 예시 2) AuthoritiesLoggingAfterFilter
@Slf4j
@Component
public class AuthoritiesLoggingAfterFilter implements Filter {
    @Override
    public void doFilter(ServletRequest req, ServletResponse res, FilterChain chain)
        throws IOException, ServletException {

        Authentication auth = SecurityContextHolder.getContext().getAuthentication();
        if (auth != null)
            log.info("User: {}, Roles: {}", auth.getName(), auth.getAuthorities());

        chain.doFilter(req, res);
    }
}
인증 성공 후 사용자와 권한을 로깅
addFilterAfter(AuthoritiesLoggingAfterFilter.class, BasicAuthenticationFilter.class)
#11. 메소드 레벨 보안
✅ 활성화 설정
@EnableMethodSecurity(prePostEnabled = true)
public class SecurityConfig { }
✅ 주요 어노테이션
| 어노테이션 | 설명 | 시점 |
|---|---|---|
@PreAuthorize | 호출 전 권한 검증 | Before method |
@PostAuthorize | 호출 후 반환 검증 | After method |
@PreFilter | 입력 필터링 | Before method |
@PostFilter | 출력 필터링 | After method |
✅ 호출 권한 부여 예시
@PreAuthorize("hasRole('USER')")
public List<Loan> findByCustomerId(Long id);
ROLE_USER가 없으면 메소드 호출 자체가 차단됩니다.
✅ 필터링 권한 부여 예시
@PreFilter("filterObject.contactName != 'Test'")
public List<Contact> saveContacts(List<Contact> contacts) { ... }

@PostFilter("filterObject.contactName != 'Test'")
public List<Contact> getContacts() { ... }
@PreFilter: 입력 데이터 중 조건에 맞는 객체만 허용
@PostFilter: 반환 리스트에서 조건 불만족 객체 제거
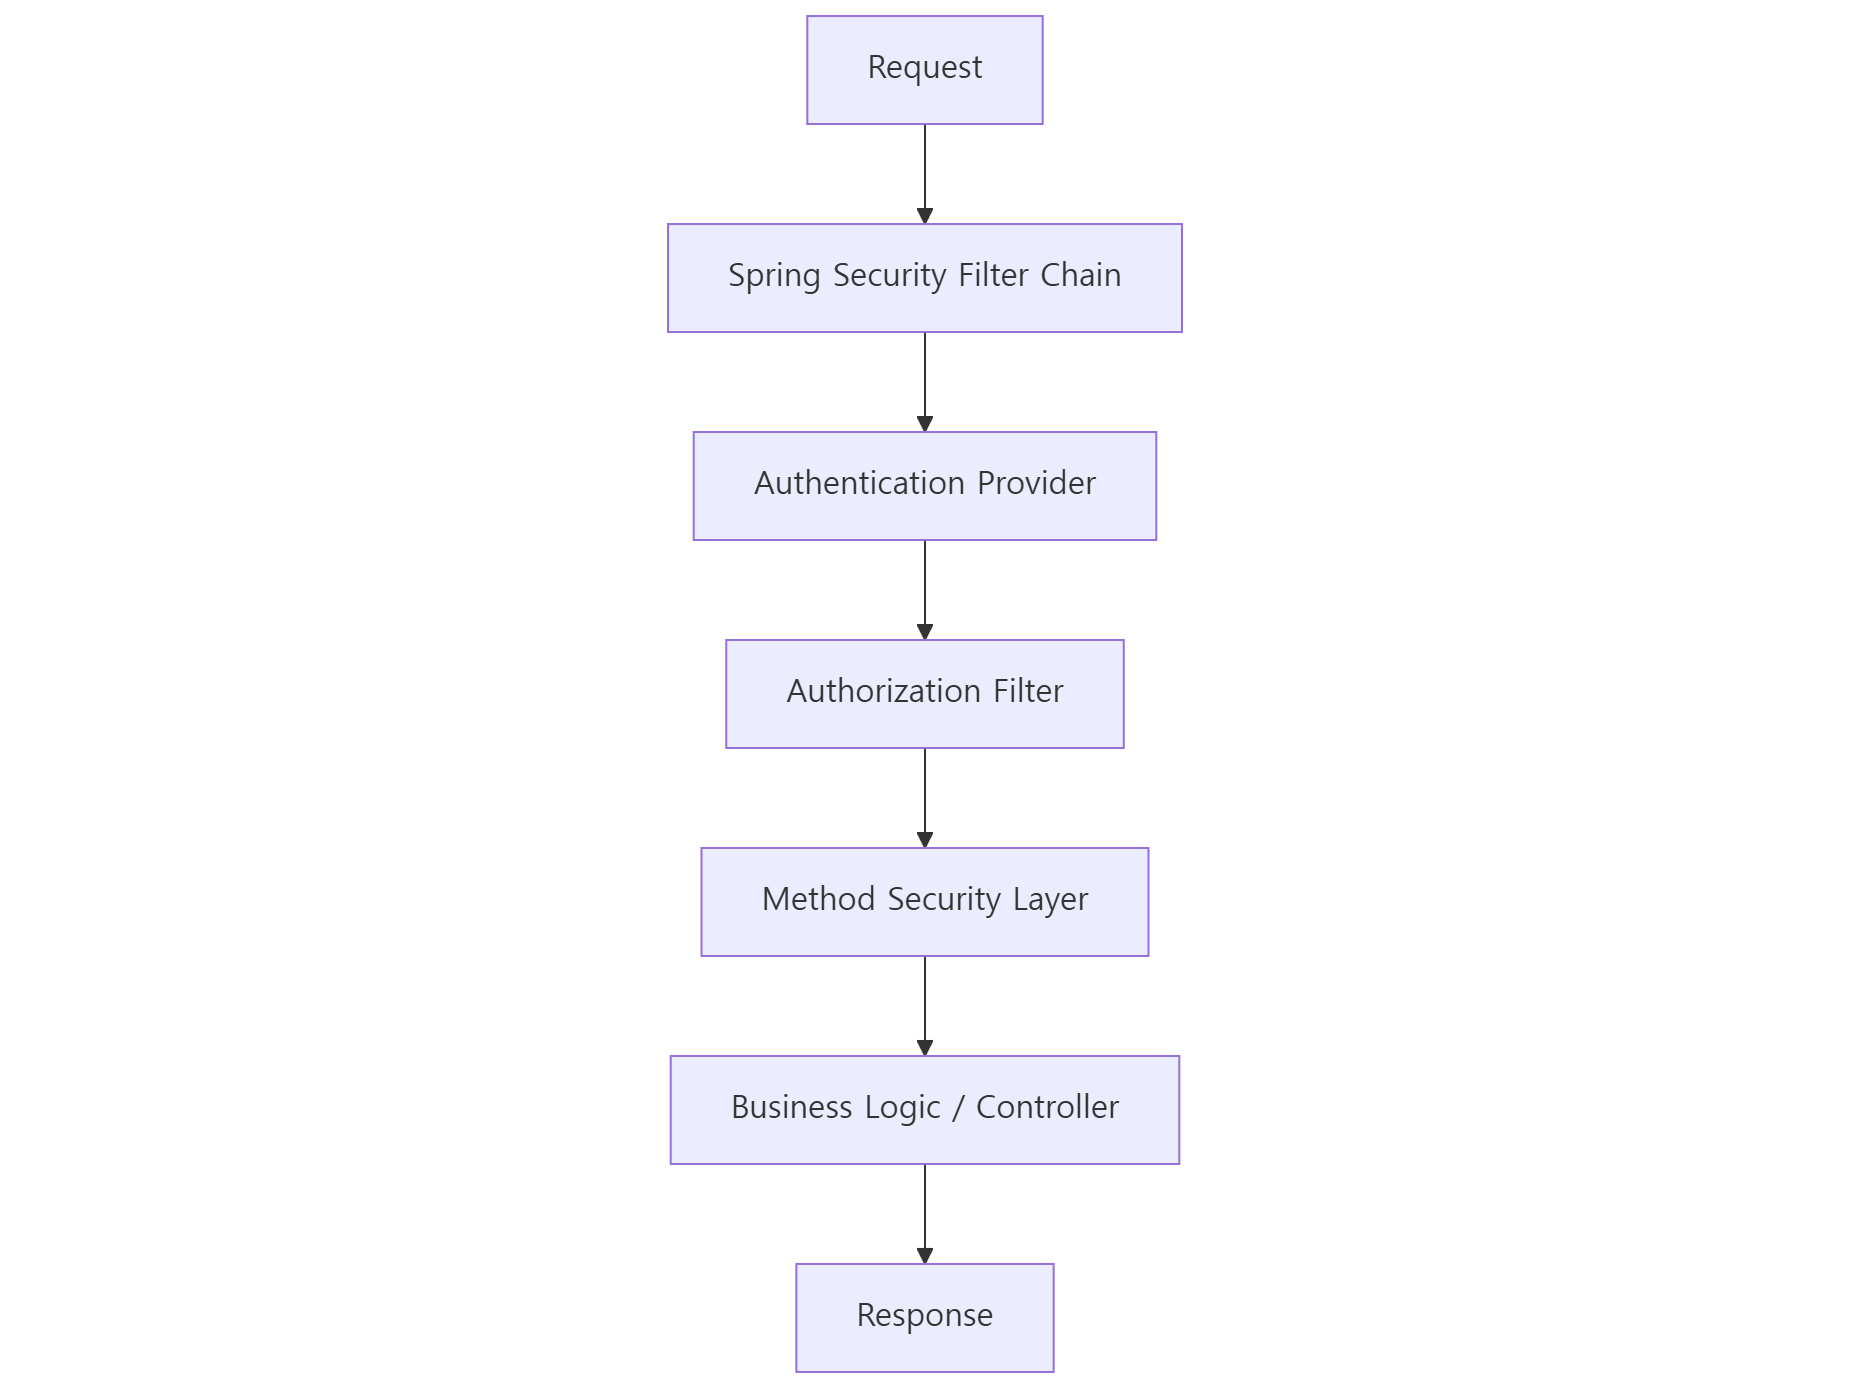
#12. 전체 구조 요약 (Mermaid)
#13. 학습 요약
| 단계 | 구성 | 목적 | 대표 예시 |
|---|---|---|---|
| 1 | 인증(Authentication) | 사용자 신원 검증 | UsernamePasswordAuthenticationFilter |
| 2 | 인가(Authorization) | 접근 허용 여부 판단 | hasAuthority(), @PreAuthorize |
| 3 | 권한 저장 | 다중 권한 저장 구조 | Customer ↔ Authority |
| 4 | 필터 체인 | 요청 전/후 커스텀 로직 삽입 | addFilterBefore, addFilterAfter |
| 5 | 메소드 보안 | 서비스/리포지토리 단 권한 제어 | @PostFilter, @PreFilter |
🧩 결론
“인증은 ‘누군가’를 증명하고,
인가는 ‘무엇을 할 수 있는가’를 통제한다.”
Spring Security의 인가 시스템은 다음을 보장합니다:
- ✅ 데이터베이스 수준의 다중 권한 관리
- ✅ API/메소드/필터 단위의 다층 보안
- ✅ 세밀한 제어가 가능한 커스텀 확장성