MSA(Spring Cloud 기반) 기술 스택과 Spring Security 6 변경 사항
1. 오늘 배운 내용
오늘은 마이크로서비스 아키텍처(MSA)에서 Spring Cloud 기술 스택의 관계와 동작 순서를 학습했다. Spring Cloud의 다양한 컴포넌트들이 어떻게 협력하여 MSA 환경에서 동작하는지 정리해보았다.
Spring Cloud 기반 MSA 서비스 흐름
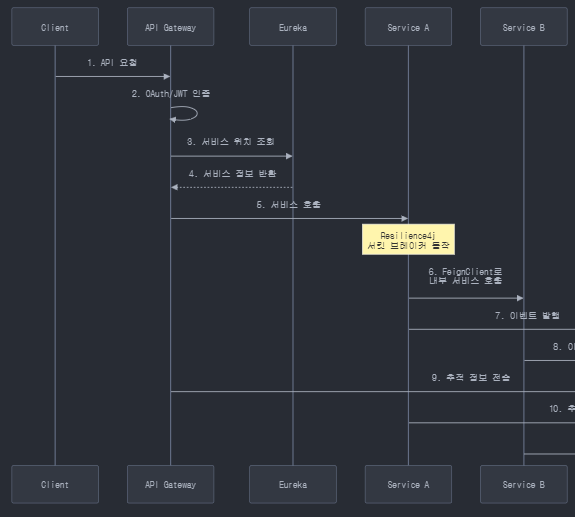
Spring Cloud의 주요 기술 스택을 모두 활용하는 경우, 서비스 간의 관계와 동작 순서는 다음과 같다.
(1) 요청 및 서비스 디스커버리
- 클라이언트(Web/Mobile) → API Gateway(Spring Cloud Gateway)를 통해 모든 요청을 전달
- API Gateway는 Eureka Server를 조회하여 적절한 서비스로 요청을 전달
- API Gateway에서 OAuth2 + JWT 인증/인가 수행
- 필터링 및 로깅(Spring Cloud Sleuth + Zipkin) 적용
(2) 서비스 검색 및 로드 밸런싱
- Eureka Server를 이용하여 동적으로 서비스 검색
- Ribbon을 활용하여 로드 밸런싱 수행
- 서비스가 동적으로 생성/종료될 수 있으므로 헬스 체크를 통해 가용한 서비스만 유지
(3) 마이크로서비스 내부 처리
- 각각의 마이크로서비스(User, Order, Product, Payment)가 독립적으로 비즈니스 로직 처리
- 서비스 간 통신 시 FeignClient + Ribbon을 사용하여 부하 분산 및 로드 밸런싱
(4) 장애 대응 및 안정성 유지
- Resilience4j 서킷 브레이커를 활용하여 장애 발생 시 서비스 간 영향을 최소화
- 장애 발생 시 Fallback 메서드를 실행하여 시스템 복구
2 오늘 마주한 오류
❌ authorizeRequests() 사용 불가
Spring Security 6에서는 authorizeRequests()가 deprecated되어 authorizeHttpRequests()로 변경됨.
기존 코드 (Spring Security 5) ❌
.authorizeRequests(authorize ->
    authorize
        .requestMatchers("/auth/signIn").permitAll()
        .anyRequest().authenticated()
)
변경 후 (Spring Security 6) ✅
.authorizeHttpRequests(auth ->
    auth
        .requestMatchers("/auth/signIn").permitAll() // 인증 없이 접근 허용
        .anyRequest().authenticated() // 나머지 요청은 인증 필요
)
🔹 차이점:
authorizeRequests()는 더 이상 지원되지 않으며,authorizeHttpRequests()를 사용해야 한다.
3. 해결 방법 및 새롭게 알게 된 점
- Spring Cloud MSA의 전체적인 서비스 호출 흐름을 명확히 이해했다.
- Spring Security 6에서 변경된
authorizeHttpRequests()적용법을 학습했다. - FeignClient + Ribbon을 활용하여 서비스 간 통신을 최적화하는 방법을 익혔다.
- 서킷 브레이커(Resilience4j)와 로깅을 적용하여 장애 발생 시 안정성을 높일 수 있음을 확인했다.
📌 결론
오늘은 Spring Cloud 기반의 MSA 아키텍처를 전체적으로 정리하고, Spring Security 6의 변경 사항을 적용하는 과정에서 발생한 오류를 해결했다.
앞으로 Spring Cloud를 활용한 고가용성, 장애 복구, 이벤트 기반 처리, 분산 추적을 더욱 깊이 학습할 필요가 있음을 깨달았다. 🚀
Dreamer